

*/
When the UK Computer Misuse Act (CMA) received Royal Assent on 29 June 1990, Elton John was at Number One with the song Sacrifice. Mr John played 10 nights at the O2 Arena this spring and headlines Glastonbury in the summer. So maybe things haven’t really changed enough to require an amendment to computer misuse legislation in the UK?
Think again. The Cray 1 Supercomputer, widely considered to be the fastest and most powerful supercomputer in the world until 1990, had slightly less processing power than an iPhone 5. There have since been another nine iterations of the iPhone meaning that almost every person in Britain now is carrying a supercomputer in their pocket more powerful than that conceived of when the CMA came into force. It is therefore unsurprising that in February 2023 the Home Office outlined reforms to the 30-year-old cybercrime law and issued a consultation for reform.
There appears to be a real international consensus to improve cybercrime law. as well The Australian Federal Government announced plans, on 6 March 2023, to overhaul the country’s cybersecurity agenda in the wake of last year’s disastrous data breaches on Optus and Medibank, which compromised the personal information of almost 10 million Australians in two of the largest attacks in the nation’s history.
The Indian Ministry of Home Affairs is working on making existing cyber laws more stringent to tackle cybercrime. And, on 10 March 2023, the United Arab Emirates announced the introduction of the first UAE Cybercrime law which will attempt to address ‘cyberattacks’ and threats in the modern world. Cyberattack, as defined under the Act, includes every intentional and planned targeting of infrastructure, networks, information systems, or information technology methods.
But unless you are practising in cyber security law, or data breaches, why is this relevant to the Bar?
These proposed reforms constitute only part of the UK government’s approach towards cyber security. Another, following the UK’s exit from the European Union, is the recapitulation of the Data Protection and Digital Information Bill (DPDIB). Brexit’s answer to GDPR, the second attempt of DPDIB was unveiled on 8 March 2023 with the strong assertion that it would save £4bn over 10 years.
While this number may sound impressive, those who have just managed to come to terms with the data protection principles contained within GDPR may not feel ecstatic by the thought of new legislation. However, the government has suggested the following three benefits which could assist chambers. But will these really help us?
Unlike GDPR, which provides a prescriptive approach to data protection procedures that must be applied, the government is suggesting that DPDIB will cut down the amount of paperwork chambers will need to produce to show compliance. The caveat, though, is for organisations ‘whose processing activities are likely to pose a high risk to individual’s rights and freedoms’. These organisations will need to continue to keep processing records including, for example, the personal data which is held, where, the security measures in place and a clear policy for deletion.
The government press release suggested organisations ‘processing large volumes of sensitive data about people’s health’ would need to continue to maintain the higher level of record keeping. In that context, chambers which process large volumes about people’s legal rights are also likely to maintain the standards imposed by GDPR.
According to Science, Innovation and Technology Secretary Michelle Donelan, the new rules will give organisations more clarity about when they can process personal data without needing consent or weighing up their own interests in processing the data against an individual’s rights for certain public interest activities. This could include circumstances where there is a public interest in sharing personal data to prevent crime, safeguard national security or protect vulnerable individuals.
This clarity may provide assistance for companies that inadvertently receive personal information that is sensitive, but potentially harmful or criminal, and want to properly process this by raising with an appropriate authority or regulator. This is unlikely to positively impact upon the Bar, however, which has always had a clear understanding of legal professional privilege and did so prior to data protection legislation and GDPR.
The government has indicated a commitment to maintaining high data protection standards and continuing the ‘free flow of personal data between like-minded countries’. The updated DPDIB is purportedly designed so that businesses can continue to use existing international data transfer mechanisms to share personal data overseas if they are already compliant with current UK data laws. This will ensure that British businesses do not need to pay more costs or complete new checks to show they are compliant with the updated rules. Chambers providing advice into foreign jurisdictions will be able to continue to provide this service and could expand into new countries if they meet the new UK rules.
The problem is that the concept of DPDIB is divergent from GDPR. If the EU considers the UK system is different and lesser, then the current ‘data adequacy status’, which protects the flow of data between both jurisdictions, would be lost. At this point chambers’ compliance with UK legislation would not be enough to continue to advise EU individuals or companies.
Will the DPDIB provide an easier future? Or will the burden on chambers remain unchanged, and providing advice into the EU become significantly more difficult? Only time will tell. And will Elton John be at Number One when we find out?
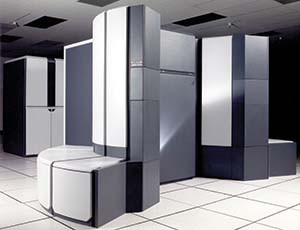
The Cray Y 190A Supercomputer (pictured above at the NASA Ames Research Center in 1990) had slightly less processing power than an iPhone 5.
Sam Thomas is a barrister at Serjeants’ Inn. He is the co-author of Cyber Security: Law and Practice (LexisNexis: 2019) and Blockchain and Cryptocurrency: International Legal and Regulatory Challenges (Bloomsbury: 2023). Sam sits on the Bar Council IT Panel and is Chair of the Association of Regulatory and Disciplinary Lawyers. Sam’s practice encompasses advocacy and advice in cyber compliance and regulatory law, for which he was recognised by Chambers & Partners and the Legal 500, 2021-25.
When the UK Computer Misuse Act (CMA) received Royal Assent on 29 June 1990, Elton John was at Number One with the song Sacrifice. Mr John played 10 nights at the O2 Arena this spring and headlines Glastonbury in the summer. So maybe things haven’t really changed enough to require an amendment to computer misuse legislation in the UK?
Think again. The Cray 1 Supercomputer, widely considered to be the fastest and most powerful supercomputer in the world until 1990, had slightly less processing power than an iPhone 5. There have since been another nine iterations of the iPhone meaning that almost every person in Britain now is carrying a supercomputer in their pocket more powerful than that conceived of when the CMA came into force. It is therefore unsurprising that in February 2023 the Home Office outlined reforms to the 30-year-old cybercrime law and issued a consultation for reform.
There appears to be a real international consensus to improve cybercrime law. as well The Australian Federal Government announced plans, on 6 March 2023, to overhaul the country’s cybersecurity agenda in the wake of last year’s disastrous data breaches on Optus and Medibank, which compromised the personal information of almost 10 million Australians in two of the largest attacks in the nation’s history.
The Indian Ministry of Home Affairs is working on making existing cyber laws more stringent to tackle cybercrime. And, on 10 March 2023, the United Arab Emirates announced the introduction of the first UAE Cybercrime law which will attempt to address ‘cyberattacks’ and threats in the modern world. Cyberattack, as defined under the Act, includes every intentional and planned targeting of infrastructure, networks, information systems, or information technology methods.
But unless you are practising in cyber security law, or data breaches, why is this relevant to the Bar?
These proposed reforms constitute only part of the UK government’s approach towards cyber security. Another, following the UK’s exit from the European Union, is the recapitulation of the Data Protection and Digital Information Bill (DPDIB). Brexit’s answer to GDPR, the second attempt of DPDIB was unveiled on 8 March 2023 with the strong assertion that it would save £4bn over 10 years.
While this number may sound impressive, those who have just managed to come to terms with the data protection principles contained within GDPR may not feel ecstatic by the thought of new legislation. However, the government has suggested the following three benefits which could assist chambers. But will these really help us?
Unlike GDPR, which provides a prescriptive approach to data protection procedures that must be applied, the government is suggesting that DPDIB will cut down the amount of paperwork chambers will need to produce to show compliance. The caveat, though, is for organisations ‘whose processing activities are likely to pose a high risk to individual’s rights and freedoms’. These organisations will need to continue to keep processing records including, for example, the personal data which is held, where, the security measures in place and a clear policy for deletion.
The government press release suggested organisations ‘processing large volumes of sensitive data about people’s health’ would need to continue to maintain the higher level of record keeping. In that context, chambers which process large volumes about people’s legal rights are also likely to maintain the standards imposed by GDPR.
According to Science, Innovation and Technology Secretary Michelle Donelan, the new rules will give organisations more clarity about when they can process personal data without needing consent or weighing up their own interests in processing the data against an individual’s rights for certain public interest activities. This could include circumstances where there is a public interest in sharing personal data to prevent crime, safeguard national security or protect vulnerable individuals.
This clarity may provide assistance for companies that inadvertently receive personal information that is sensitive, but potentially harmful or criminal, and want to properly process this by raising with an appropriate authority or regulator. This is unlikely to positively impact upon the Bar, however, which has always had a clear understanding of legal professional privilege and did so prior to data protection legislation and GDPR.
The government has indicated a commitment to maintaining high data protection standards and continuing the ‘free flow of personal data between like-minded countries’. The updated DPDIB is purportedly designed so that businesses can continue to use existing international data transfer mechanisms to share personal data overseas if they are already compliant with current UK data laws. This will ensure that British businesses do not need to pay more costs or complete new checks to show they are compliant with the updated rules. Chambers providing advice into foreign jurisdictions will be able to continue to provide this service and could expand into new countries if they meet the new UK rules.
The problem is that the concept of DPDIB is divergent from GDPR. If the EU considers the UK system is different and lesser, then the current ‘data adequacy status’, which protects the flow of data between both jurisdictions, would be lost. At this point chambers’ compliance with UK legislation would not be enough to continue to advise EU individuals or companies.
Will the DPDIB provide an easier future? Or will the burden on chambers remain unchanged, and providing advice into the EU become significantly more difficult? Only time will tell. And will Elton John be at Number One when we find out?
The Cray Y 190A Supercomputer (pictured above at the NASA Ames Research Center in 1990) had slightly less processing power than an iPhone 5.

The Chair of the Bar reports back
Clement Cowley, Partner at The Penny Group, explains how global events can influence the performance of pensions and ISAs, and why taking a long-term approach to investing is often the most effective strategy
Mário Barroso, Head of R&D and Method Development at AlphaBiolabs, discusses what family law professionals need to know about hallucinogens, from the main hallucinogenic drugs encountered in family proceedings, to their effects and the testing options available
Harmony Christian Ministries is the latest charity to benefit from a £500 donation from AlphaBiolabs via the company’s Giving Back initiative
By David Green
Mário Barroso, Head of R&D and Method Development at AlphaBiolabs, examines the forensic science underpinning hair drug testing, its evidential scope and limitations, and why it remains the gold standard for evidencing patterns of drug use in family proceedings
At the start of her term, Chair of the Bar 2026 Kirsty Brimelow KC set out a series of priorities for the year ahead. One of those priorities was children in the justice system
As the world becomes more digital, Barbara Vinagre Mota examines international research into the mental health consequences of judges’ exposure to graphic and immersive evidence, highlighting the importance of support systems
In an era of patient-centred care and growing concern over misconduct in medical settings, why do women still lack the right to choose women consultants for examination and treatment? Charles Davey investigates
Reviewed by Daniel Barnett
James McNeill Whistler at Tate Britain until 27 September Rothko in Florence at Palazzo Strozzi until 23 August Reviewed by Stephen Cragg KC